

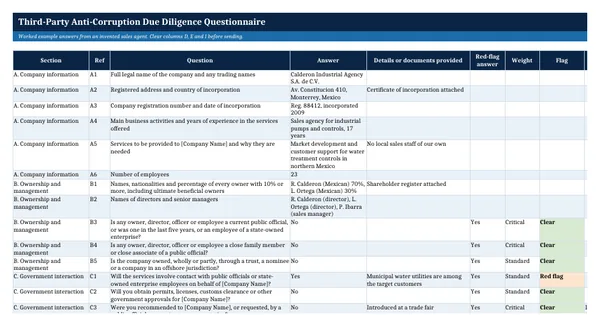
 Excel workbook preview
Anti-bribery (FCPA, UK Bribery Act)
FCPA Red Flags Checklist
3 free downloads per account. Just your email and a 6-digit code.
About this template
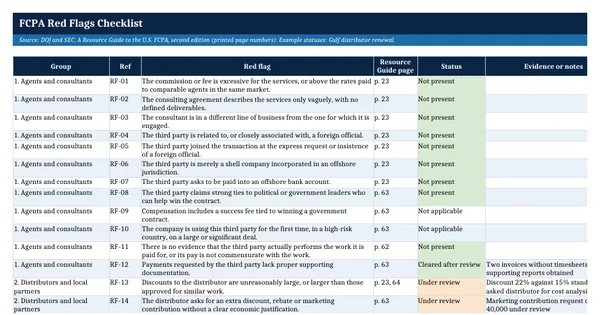
An FCPA red flags checklist helps a reviewer test a third party, a transaction or a set of payments for the warning signs US prosecutors and the SEC associate with bribery. Red flags do not prove a bribe, but a company that ignores them can be treated as knowing, because the FCPA reaches conscious disregard. Auditors and compliance teams use the list before approving agents, renewals, large discounts and unusual payments.
The workbook lists 48 red flags in seven groups, each written as a checkable statement and tied to the page of the DOJ and SEC Resource Guide to the FCPA, second edition, where it appears. The sources include the third-party red flags list, the hypotheticals on consultants and distributors, the gift and travel examples, the five charitable questions and the list of ways bribes have been mischaracterized in the books.
Who it is for
The compliance analyst, controller or internal auditor who must check a third party, deal or set of payments for bribery warning signs and document the result.
What is inside
- 48 red flags in 7 groups: agents, distributors, gifts and travel, charities, payments and records, program signals, acquisitions
- Each red flag cites the page of the DOJ and SEC Resource Guide to the FCPA, second edition, it comes from
- Status dropdown with five values and colour: Not present, Cleared after review, Under review, Unresolved, Not applicable
- Worked example statuses for a distributor renewal review, ready to clear
- Summary sheet with review details, counts per group and status, and an overall result formula
- Overall result shows Stop, Hold, Incomplete or Proceed from the statuses
- How to use sheet, freeze panes, filters and landscape print fit
How to use it
Fill in the review details on the Summary sheet, clear the example statuses, then mark each red flag with evidence.
Files
- XLSXfcpa-red-flags-checklist.xlsx14 KB
Opens in Microsoft Word or Excel, Google Docs or Sheets, and LibreOffice. Built on free, official texts that anyone can read: laws, regulations, standards and guidance published by public bodies. A template to adapt, not legal, tax or accounting advice.
Questions about this template
What are the most common FCPA red flags with third parties?
The DOJ and SEC Resource Guide lists excessive commissions, unreasonably large discounts to distributors, vaguely described consulting services, a consultant in a different line of business, a third party related to or recommended by an official, an offshore shell company and requests for payment to offshore accounts. All eight are in the first two groups of this checklist.
What should happen when a red flag is found?
A red flag means stop and look closer, not automatically reject. Record it as Under review, gather evidence and decide whether it can be explained. If it is explained and documented, mark it Cleared after review. If it cannot be resolved, mark it Unresolved, and the overall result on the Summary sheet tells the reviewer to escalate to the chief compliance officer.
Is this checklist only for US companies?
The red flags come from the US Resource Guide, but the same warning signs matter under the UK Bribery Act 2010 and most other anti-corruption laws. A UK or European company can use the checklist as part of its due diligence and monitoring, alongside the Ministry of Justice guidance on adequate procedures.
More Anti-bribery (FCPA, UK Bribery Act) templates
Anti-bribery (FCPA, UK Bribery Act)
Anti-Bribery and Corruption Policy Template (FCPA, UK Bribery Act)
Anti-bribery (FCPA, UK Bribery Act)
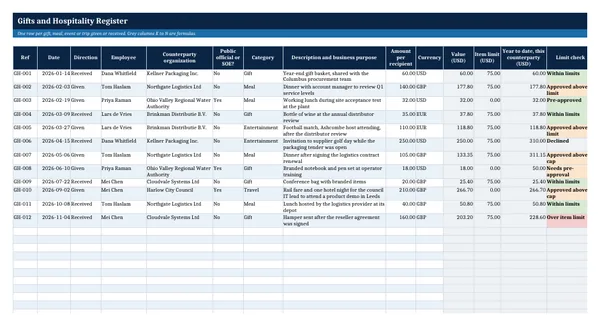
Gifts and Hospitality Register
Anti-bribery (FCPA, UK Bribery Act)
Gifts and Entertainment Policy
Anti-bribery (FCPA, UK Bribery Act)