

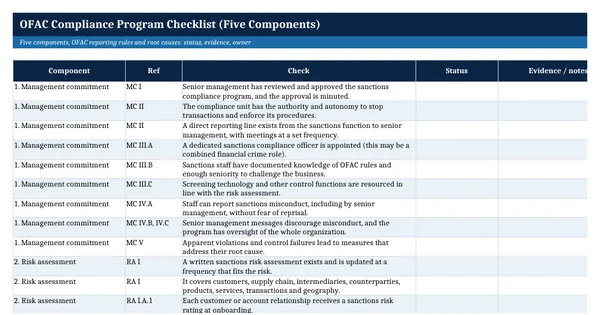
 Excel workbook preview
OFAC Compliance Program Checklist (Five Components)
3 free downloads per account. Just your email and a 6-digit code.
About this template
An OFAC compliance program checklist turns the published expectations into statements a reviewer can tick or not. It is used for an annual self-assessment, before an independent test, during bank onboarding, or when a new compliance officer takes over and needs to know where the program stands.
This checklist follows the five components and numbered items in OFAC's A Framework for OFAC Compliance Commitments, adds the reporting and recordkeeping rules in 31 CFR 501.601 to 501.604, and ends with checks drawn from the root causes OFAC lists in the framework's appendix. Each item shows its reference so the evidence can be traced to the source.
Who it is for
The compliance officer or internal auditor who has to assess the sanctions program against OFAC's framework before the bank, buyer or board asks.
What is inside
- 50 checkable statements in 7 groups: the five OFAC components, reporting and recordkeeping, and root causes
- References to the framework item (for example MC III.A) or the 31 CFR section for every check
- Status dropdown with 5 values and green, amber and red highlighting
- Coverage percentage that excludes items marked not applicable
- Summary sheet with items and implemented share per group, all formulas
- Evidence and owner columns, freeze panes, filter and print fit
- How to use sheet with the source list and the affiliation note
How to use it
Work through each group with the people who run the control, and record the evidence you would show a reviewer next to every status.
Files
- XLSXofac-compliance-program-checklist.xlsx12 KB
Opens in Microsoft Word or Excel, Google Docs or Sheets, and LibreOffice. Built on free, official texts that anyone can read: laws, regulations, standards and guidance published by public bodies. A template to adapt, not legal, tax or accounting advice.
Questions about this template
What does OFAC look for in a sanctions compliance program?
The 2019 framework sets out five components: senior management commitment, a routine risk assessment, internal controls including written procedures and recordkeeping, independent testing and auditing, and training at least once a year. It also lists root causes of past violations, such as screening software faults and weak ownership due diligence, which this checklist turns into checks.
How is the coverage percentage calculated?
The coverage cell divides the number of items marked Implemented by the number of items minus those marked Not applicable. Partially implemented and planned items do not count as implemented. The Summary sheet shows the same measure for each of the seven groups, so the weakest component is visible at a glance.
How often should an OFAC compliance program be tested?
The framework asks for testing or audit appropriate to the level and sophistication of the program, carried out by a function that is independent of the activities it tests. It does not fix a frequency. Many organizations run a self-assessment like this one every year and an independent test on a cycle set by their risk assessment.
More Sanctions compliance (OFAC) templates
Anti-bribery (FCPA, UK Bribery Act)
Anti-Bribery and Corruption Policy Template (FCPA, UK Bribery Act)
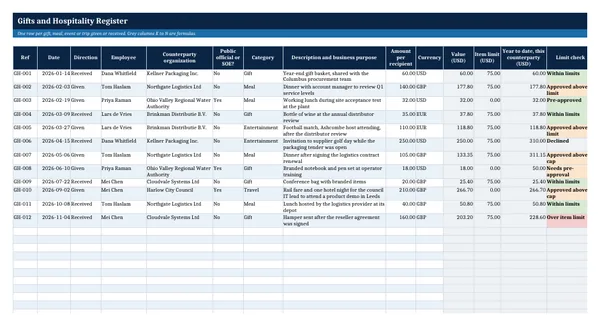
Anti-bribery (FCPA, UK Bribery Act)
Gifts and Hospitality Register
Anti-bribery (FCPA, UK Bribery Act)
Gifts and Entertainment Policy
Anti-bribery (FCPA, UK Bribery Act)