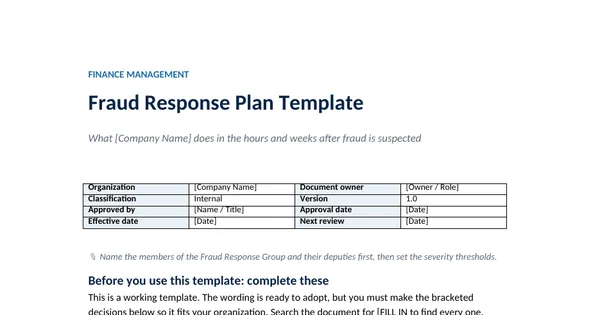
 Word document preview
Fraud Response Plan Template
3 free downloads per account. Just your email and a 6-digit code.
About this template
A fraud response plan is the procedure an organization follows from the moment fraud is suspected: who is told, how evidence is protected, who investigates, how losses are stopped and recovered, and who outside the organization must be notified. Insurers, auditors and audit committees ask for it because the first days decide how much is recovered and whether the evidence holds.
GAO-15-593SP lists a plan for responding to identified instances of fraud as a leading practice, with a prompt and consistent response and referral to the appropriate authorities. This template turns that into a seven-step first 72 hours, three severity levels, evidence and containment steps, a notifications table and closure rules that feed lessons back into the fraud risk assessment.
Who it is for
The CFO or fraud risk lead who was asked by the audit committee or the insurer what happens on day one when fraud is found, and had no written answer.
What is inside
- 9 body sections plus roles and a testing and maintenance section, about 1,250 words
- First 72 hours table with 7 steps, each with an owner and timing
- Severity table with 3 levels setting who investigates and who is told
- Evidence preservation and containment lists, including bank recall and insurance notice
- Notifications table with 6 parties, citing 2 CFR 200.113, FAR 52.203-13 and GDPR Article 33
- Closure and lessons learned rules tied to GAO-15-593SP leading practice 4.3
- Fraud Response Group and other roles in a roles table
How to use it
Name the members of the Fraud Response Group and their deputies first, then set the severity thresholds.
Files
- DOCXfraud-response-plan-template.docx41 KB
Opens in Microsoft Word or Excel, Google Docs or Sheets, and LibreOffice. Built on free, official texts that anyone can read: laws, regulations, standards and guidance published by public bodies. A template to adapt, not legal, tax or accounting advice.
Questions about this template
What should happen in the first 24 hours after fraud is suspected?
Log the report, check the response team for conflicts of interest, assess credibility and severity, issue a legal hold, and contain the loss by blocking vendors, suspending access or asking the bank for a recall. Nobody confronts the suspect or moves records before evidence is secured.
Who should lead a fraud investigation?
It depends on severity. Small cases can be led by the fraud risk lead, larger ones with internal audit, and cases involving senior management or the financial statements by outside counsel with forensic accountants. Nobody investigates their own team or their own manager.
Do we have to report fraud to anyone outside the company?
Sometimes. Federal award recipients have a written disclosure duty under 2 CFR 200.113, and contractors whose contracts include FAR 52.203-13 must disclose credible evidence to the agency Inspector General. A personal data breach may need notice to the data protection authority, and the insurer usually has a notice period.