 Word document preview
SOX Compliance Policy Template
3 free downloads per account. Just your email and a 6-digit code.
About this template
A SOX compliance policy is the board-approved document that says how a public company meets its duties under sections 302, 404 and 906 of the Sarbanes-Oxley Act. Auditors and audit committees ask for it in the first year after listing, and again when a deficiency shows the program has no written rules. It sets who owns the controls, how they are tested, how the certifying officers get comfort each quarter and how problems are escalated.
The template has fifteen numbered sections, including roles and a policy close. A legal basis table ties each duty to the statute and the SEC rule that implements it, such as Rules 13a-14 and 13a-15 and Items 307 and 308 of Regulation S-K. The definitions come from Rule 12b-2. The assessment approach follows the SEC's 2007 interpretive guidance for management, Release 33-8810. Worked tables show the annual calendar, the quarterly certification timetable and the escalation of deficiencies.
Who it is for
The controller or CFO of a newly listed or listing company whose auditor or audit committee asked for the written policy behind the SOX program and found none.
What is inside
- 15 numbered sections, including roles and a policy close (compliance, exceptions, review)
- Legal basis table: 8 requirements mapped to SOX, the SEC rule and an owner
- Definitions of disclosure controls, ICFR, significant deficiency and material weakness from SEC rules
- Annual assessment calendar by quarter with the output of each step
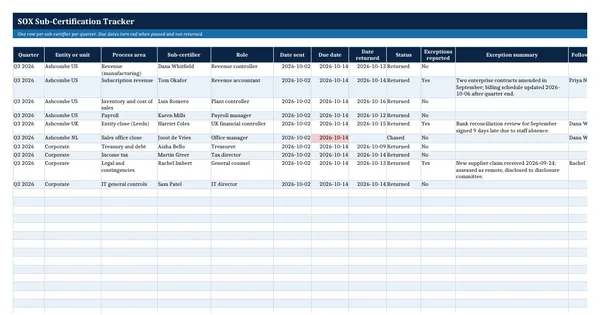
- Quarterly certification timetable in 6 steps, from sub-certification to signing
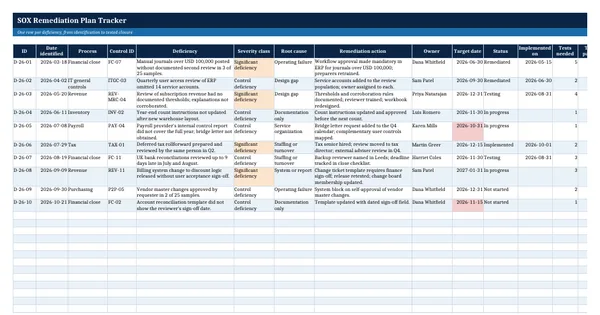
- Escalation table for 4 deficiency classes: who is told, when, and what is disclosed
- Roles table for 9 roles, from audit committee to control owners
- Checklist of 7 decisions to make before adoption
How to use it
Name the control framework, the in-scope entities and the policy owner, then take the policy to the audit committee for approval.
Files
- DOCXsox-compliance-policy-template.docx42 KB
Opens in Microsoft Word or Excel, Google Docs or Sheets, and LibreOffice. Built on free, official texts that anyone can read: laws, regulations, standards and guidance published by public bodies. A template to adapt, not legal, tax or accounting advice.
Questions about this template
What should a SOX compliance policy cover?
It should state the legal duties under sections 302, 404 and 906, define disclosure controls and internal control over financial reporting, set documentation and testing standards, describe the quarterly certification process, and say how deficiencies are classified, escalated and remediated. It also names the roles, from the audit committee to the control owners, and how often the policy is reviewed.
Does the SEC require a specific control framework?
No single framework is named in the rule. Rule 13a-15(c) requires management to evaluate internal control over financial reporting against a suitable, recognized control framework established by a body that followed due process, including public comment. Management names the framework it used in its annual report under Item 308(a)(2).
Can management call internal control effective with a material weakness?
Not as of year end. Item 308(a)(3) of Regulation S-K says management may not conclude that internal control over financial reporting is effective if one or more material weaknesses exist. The SEC's 2007 guidance notes that a weakness remediated before year end can still support an effective conclusion, with disclosure considered.